


The guide explains what is DNS over HTTPS (DoH), its key benefits, limitations, and whether users should keep using DNS over HTTPS on or off.
Every time a user visits a website, their device needs to find the website's server before the page can load. DNS helps translate human-readable domain names into IP addresses, while technologies such as What Is a CDN can help deliver website content efficiently from servers closer to users.
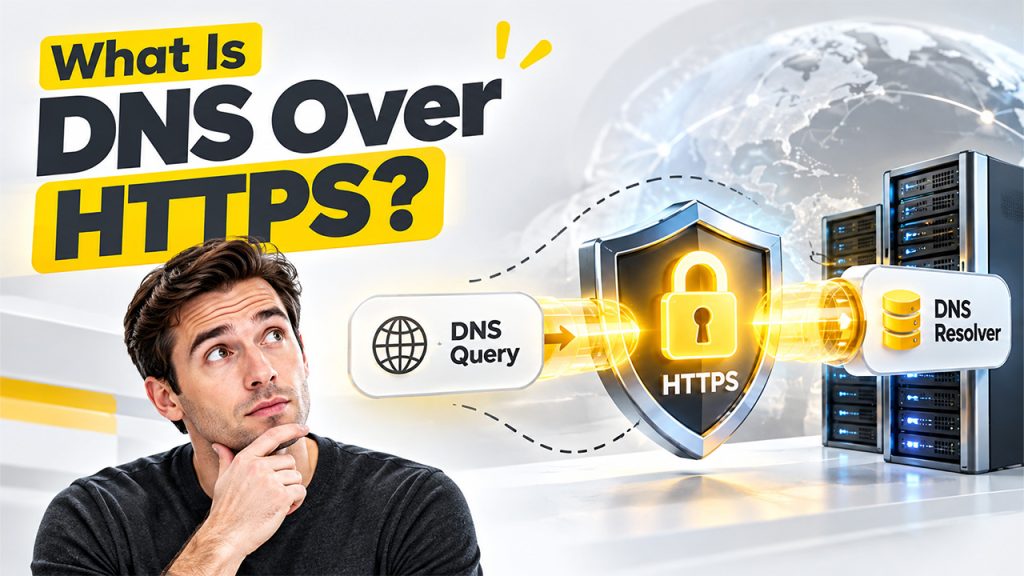
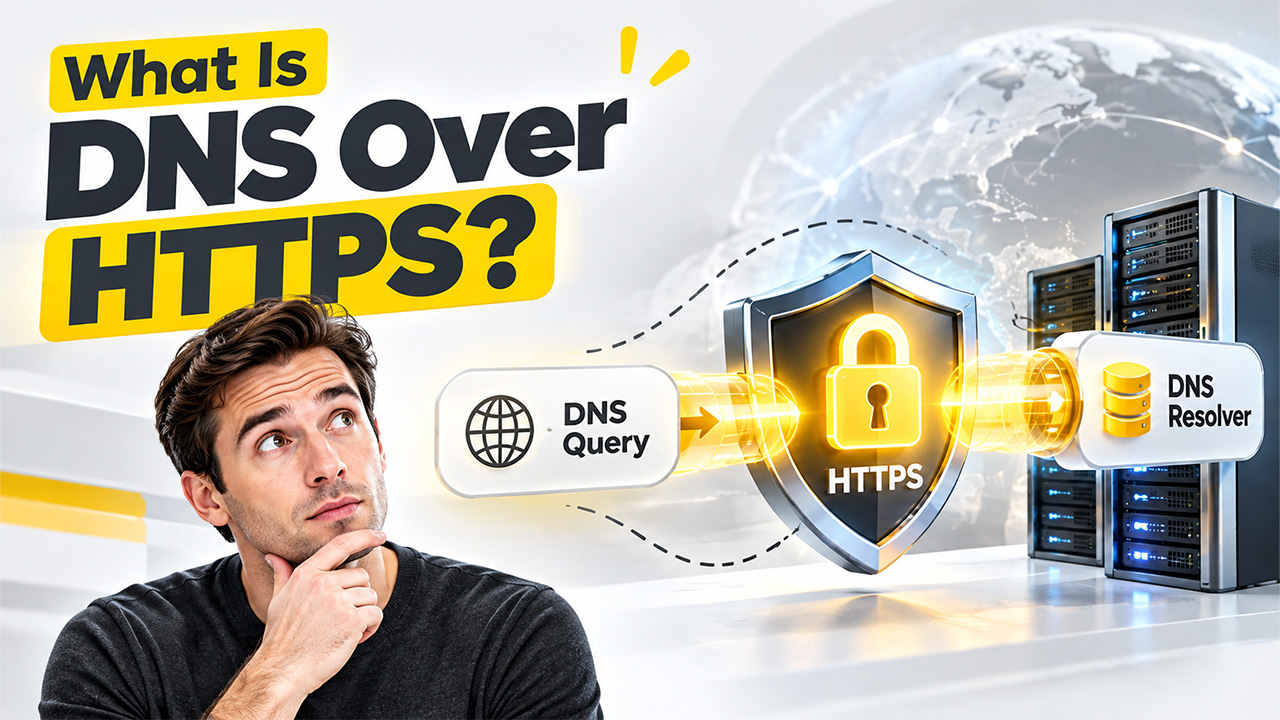
This process generally involves the Domain Name System (DNS), which helps translate human-readable domain names into IP addresses that the devices can understand. Traditionally, DNS queries are sent without encryption, which means that they can be viewed or manipulated while traveling between the user's device and a DNS resolver. DNS over HTTPS, or DoH, addresses this problem by sending DNS queries through an encrypted HTTPS connection.
But it is essential to understand what is DNS over HTTPS, how it works, and whether the user turns it on or off.
What Is DNS Over HTTPS?
DNS Over HTTPS, or DoH, is a technology that encrypts DNS queries and sends them over an HTTPS connection. When a user enters a website address into their browser, the device performs a DNS lookup to determine the IP address that is associated with that domain. With traditional DNS, these queries are generally sent using the DNS protocol over UDP or TCP.
With DoH, the DNS query is sent to a compatible DNS resolver through an encrypted HTTPS connection. The encryption helps prevent any third party on the network from easily seeing the DNS queries being transmitted between the device and the DoH resolver.
The device needs to discover the corresponding IP address. If DoH is enabled, the DNS request is encrypted before it is transmitted to the DNS resolver. The resolver also processes the request and returns the DNS response through the encrypted connection.
Key Features DNS Over HTTPS
DNS over HTTPS (DoH) improves the privacy and security of DNS by sending DNS queries through an encrypted HTTPS connection.
Some of the key features of DNS Over HTTPS are as follows:
- Encrypted DNS Queries
The main feature of DoH is encryption. DoH sends the DNS requests over HTTPS, instead of sending them as conventional and unencrypted DNS traffic.
- Uses HTTPS
DoH uses HTTPS, the same protocol that is used to secure many websites and online services. DNS queries are sent to a DoH-compatible resolver through an HTTPS connection.
- Improves Privacy
Traditional DNS queries can be observed by someone with access to network traffic. DoH encrypts the connection between the client and resolver, making it difficult for the local network observers to inspect individual DNS requests.
- Authentication and Integrity
HTTPS provides mechanisms that help authenticate the server the user is communicating with and protect data from being modified in transit.
Benefits of DNS Over HTTPS
DNS Over HTTPS offers several privacy and security benefits, which are listed below:
- Improves DNS Privacy
DoH encrypts the DNS queries between the device and the DNS resolver, making it difficult for third parties on the network to inspect the DNS activity of the user.
- Better Protection on Public Wi-Fi
As DoH encrypts DNS communication, it offers an extra layer of protection when the user is using public networks.
- Protection Against DNS Manipulation
DNS traffic can also be intercepted and manipulated by attackers. DoH helps reduce this risk by protecting communication between the device and the DNS resolver with HTTPS encryption.
- Helps Prevent Certain DNS-Based Attacks
As DoH protects DNS queries in transit, it can make certain forms of DNS interception and tampering more difficult.
- Uses Existing HTTPS Infrastructure
DoH uses HTTPS, typically over port 443. This means DNS queries can travel through the same general encrypted web infrastructure used by many other internet services.
How Does DNS Over HTTPS Works?
DNS Over HTTPS (DoH) works by sending DNS queries through an encrypted HTTPS connection instead of sending them as traditional, unencrypted DNS traffic.
The detailed process of how DNS Over HTTPS works is as follows:
- Enter the Website Address
The browser needs to know the website's IP address before it can establish a connection with the web server.
- The Device Creates a DNS Query
The device creates a DNS query that asks for the IP address associated with the website. With DoH enabled, the query is instead prepared to be sent through an HTTPS connection.
- The DNS Query Is Encrypted
The DoH client sends the DNS request over an HTTPS-encrypted connection. This encryption helps prevent someone from monitoring the network from easily reading the DNS query.
- The DoH Resolver Receives the Request
The encrypted request reaches a DNS resolver that supports DoH. The resolver decrypts and processes the request, then performs the required DNS lookup.
- The Resolver Sends the DNS Response
Once the resolver finds the requested DNS information, it sends the response back through the established HTTPS connection.
- The Device Receives the IP Address
The browser receives the DNS response and obtains the IP address that is associated with the domain.
If DNS resolution is taking longer than expected, users can learn How to Fix Slow DNS Lookup and identify potential issues with their DNS configuration, resolver, or network connection.
- Browser Connects to the Website
After DNS resolution is complete, the browser connects to the website's server.
Do I Enable DNS Over HTTPS?
Users often wonder, "Do I enable DNS over HTTPS?" The answer usually depends on the privacy, security, and network requirements of the user. For many individual users, enabling DoH can be a sensible privacy improvement, particularly when using untrusted networks such as public Wi-Fi. However, there are situations where you may want to leave it disabled.
Before enabling DoH, users should consider the following:
- Who will provide your DoH service?
- Does your organization require a specific DNS server?
- Do you use parental or security filtering based on DNS?
- Does your network administrator manage DNS centrally?
- Does your browser or operating system support DoH?
How to Enable DNS Over HTTPS
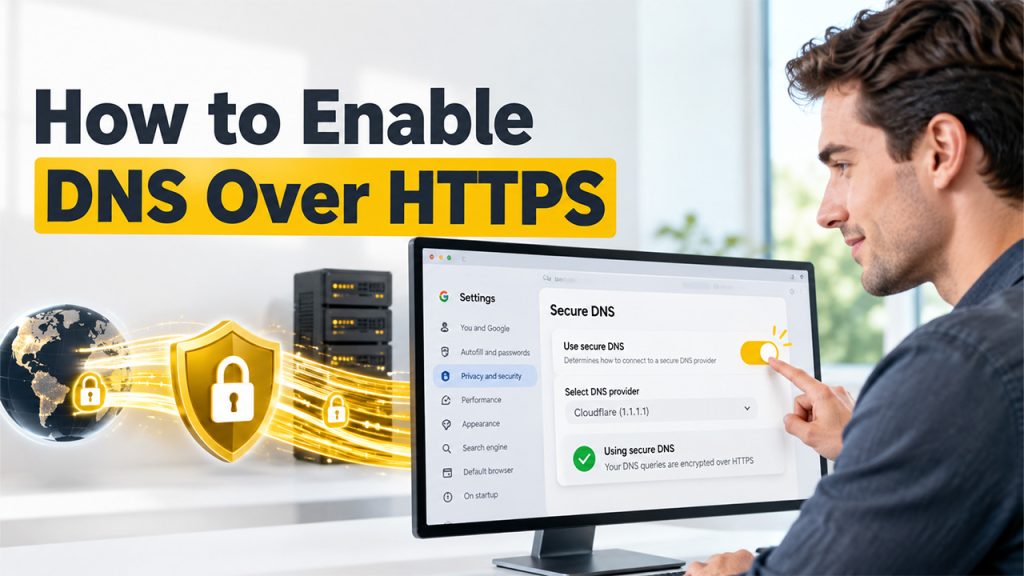
Enabling DNS Over HTTPS (DoH) encrypts DNS queries between the device or browser and a compatible DNS resolver. To enable DNS over HTTPS, users can follow the given steps:
Enable DoH in Browser
- Open your browser's Settings.
- Search for DNS, Secure DNS, or DNS over HTTPS.
- Find the option for using a secure DNS provider.
- Turn the feature On.
- Choose a preferred DNS provider if the browser gives that option.
- Save the settings and restart the browser if necessary.
Enable DoH at the Operating-System Level
If DoH is available at the operating-system level, you can generally:
- Open the device's Network or Internet Settings.
- Select the active network connection.
- Open its DNS settings.
- Look for an option such as Encrypted DNS, DNS over HTTPS, or a similar setting.
- Select a compatible DNS provider or enter the required DNS configuration.
- Save the changes.
Choose a Trusted DNS Provider
Consider factors such as:
- Privacy policies
- Logging practices
- Reliability and uptime
- Security features
- Geographic availability
- Whether the provider offers filtering or malware protection
Check Whether DoH Is Working
After enabling DoH, you can use a DNS or browser security test to verify that encrypted DNS is being used.
When making changes to DNS settings or records, users may also encounter DNS Propagation, which refers to the time it can take for DNS changes to become available across different DNS resolvers and networks.
Downsides to DNS Over HTTPS
Although DNS Over HTTPS (DoH) improves the privacy and security of DNS queries, it also has some potential disadvantages.
Some of the major downsides of DNS over HTTPS are listed below:
- Make DNS Management More Difficult
DoH can bypass the DNS configuration that is provided by the local network. This can make network management and troubleshooting more complicated.
- Interfere With DNS-Based Filtering
Various organizations use DNS filtering to block malicious or inappropriate domains. If a device sends DNS requests directly to an external DoH provider, those requests may bypass the DNS filtering system.
- Doesn't Provide Complete Online Anonymity
DoH primarily protects DNS queries between the device and the resolver. It does not hide the IP address from websites, encrypt all internet traffic, prevent browser or website tracking, replace a VPN, or make users completely anonymous online.
Conclusion
DNS Over HTTPS, or DoH, adds an important layer of privacy and security simply by encrypting DNS queries between a device and its DNS resolver. While it can help protect DNS activity from network observers and reduce the risk of DNS manipulation, it does not provide complete online anonymity or replace a VPN. Whether DNS Over HTTPS should be on or off ultimately depends on your privacy needs, network configuration, and the DNS provider you trust. By understanding how DoH works, its benefits, and its limitations, you can make an informed decision about whether to enable it.